RELEASE HIGHLIGHTS
A fairly large Quality of Life release with many fixes, optimisations and other improvements.
NEW ADA AI CAPABILITIES
Ada can now answer two new questions.
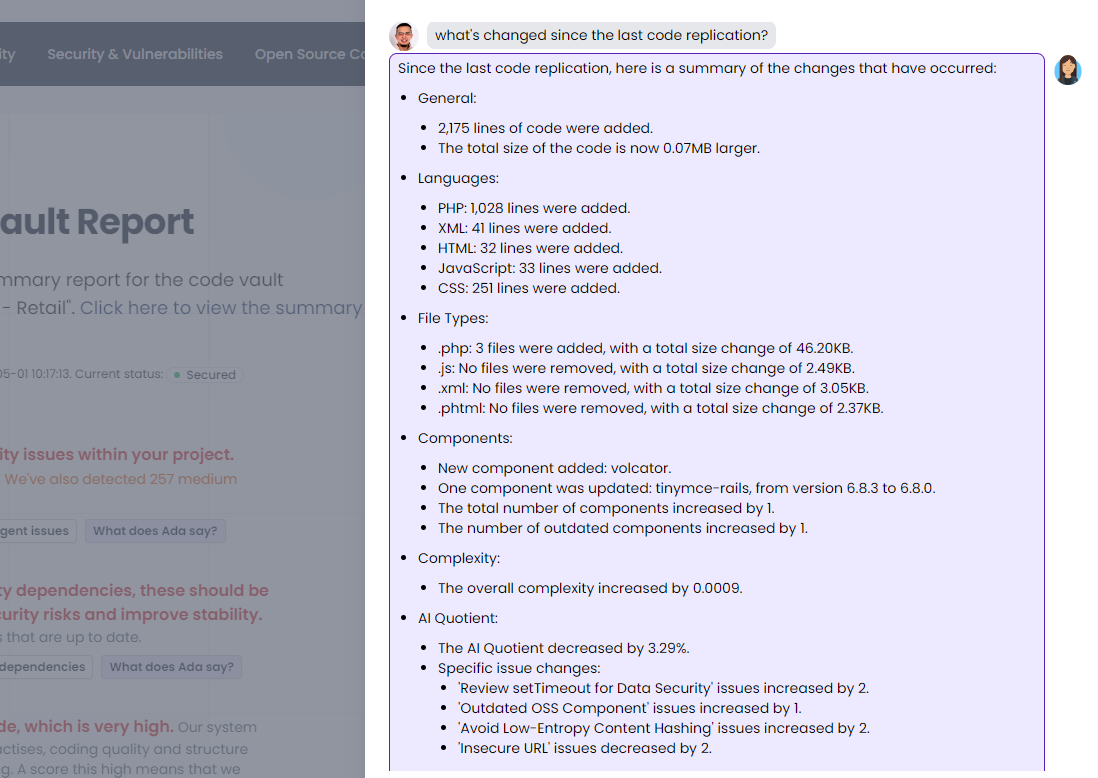
What’s changed since the last replication / code sync?
This question can only be asked at the single code vault level (not at the overall project level). It’s simple yet powerful: say you have code replication set to replicate and analyze your code once per month — with this question, Ada reviews everything that’s changed between the last code replication and the latest one, and summarises it in an easy-to-understand answer.
ADA'S ANSWER REVIEWS
Lines of code added
Total code source size (in MB)
Language changes
File type changes
Open source component changes (components added, removed, and versions changed)
Code complexity changes
AIQ (code quality) changes, including a summary of what issue types were increased or decreased
Security issue changes, including new security issue types detected or no longer detected
GIT changes (how many contributors, new contributors, who has made new changes, examples of recent change messages)
"Cost to Replicate" valuation changes
~5 sec
Time needed for Ada to give you this answer. How long would it take you to gather this data yourself?
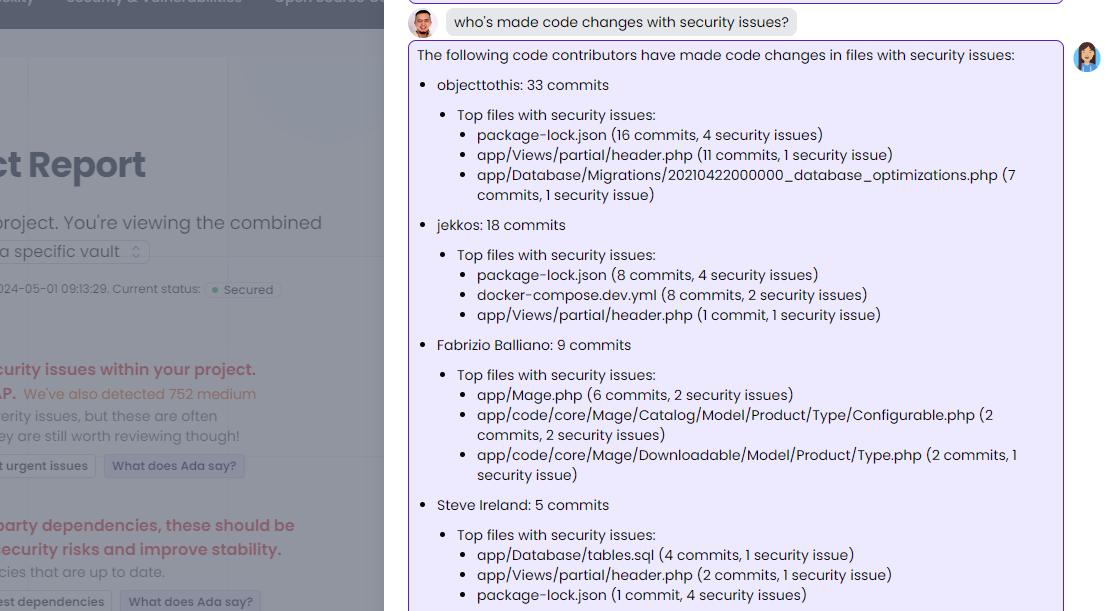
Who’s made code changes with security issues?
This is a very interesting question which compares changes made by code contributors with detected security vulnerabilities. If a developer has been working on a file with detected security vulnerabilities, Ada will flag them in the response. This disclaimer is included, and it’s important
Please note that this information is based on file paths and may not be 100% accurate. It provides an approximation of the code contributors who have made changes in areas with potential security vulnerabilities.
This data doesn’t mean that these code contributors caused the detected issues, but it could be used to start a conversation with that code contributor, or a deeper dive into the code changed and the detected issue and how / if they are related.
OTHER CHANGES
Refactored the Mechanism Used to Load Project / Vault Data While It’s Still Being Analysed
When you add a project / vault and you’re waiting for it to be analysed, you see widgets and facets of data with a loading animation, which checks for results every little while and updates the page once the data is ready. This needed to be optimised as we scale, and it’s now done — smoother, more optimal, and using fewer resources behind the scenes.
THE INCIDENT
Improvements to Our New User Onboarding Process
We’ve made the following improvements to make the experience better
Options to set your user’s name and team name.
Field values are saved in case you need to continue later.
Start with an empty project, if you need to come back after getting your code source details.
Connections to GitHub and GitLab using our native integrations now return you to the exact same page and onboarding section to continue where you were (previously you had to connect from your team settings page).
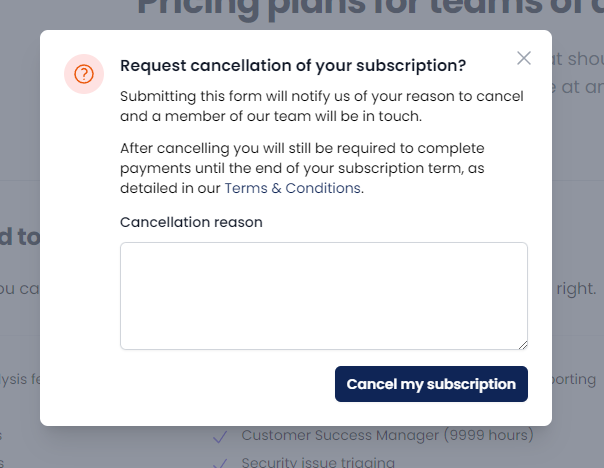
Simplifying the Subscription Cancellation Process
There is a new cancellation form in the team billing area to simply submit your cancellation request and cancel your subscription.
Dynamic Homepage Layout for Displaying More Projects
The main app homepage is now dynamic — if you have more than 10 projects, they display in a more traditional table format to make it easier to find the project you’re looking for. If you have more than 20 projects, there is also a project search function.
BUG FIXES
- Fixed a bug in the team settings functionality, where in some cases a team member would receive an automated email PDF report for a project they didn’t have access to.
- Similar to above, fixed an issue where a team member could receive emails relating to “broken code source credentials” for a project they don’t have access to.
- Fixed a bug where the number of projects / vaults a team member has access to could be inaccurate in some cases.
- Fixed a bug in the main app navigation where the “add code vault” button would sometimes not show for a project with many code vaults.
FROM COMPLEXITY TO CLARITY
Move from uncertainty to complete code confidence.
Get the independent intelligence you need to understand, verify and protect your software.
Book a demo