RELEASE HIGHLIGHTS
This release contains our new advanced security issue triaging functionality!
ADVANCED SECURITY ISSUE MANAGEMENT
An entire re-working of how users view and manage detected security issues.
We’ve been hard at work implementing a lot of new features in our security issue management area. What started as a few nice new features turned into an entire re-working of how users can view and manage the security issues our platform detects.
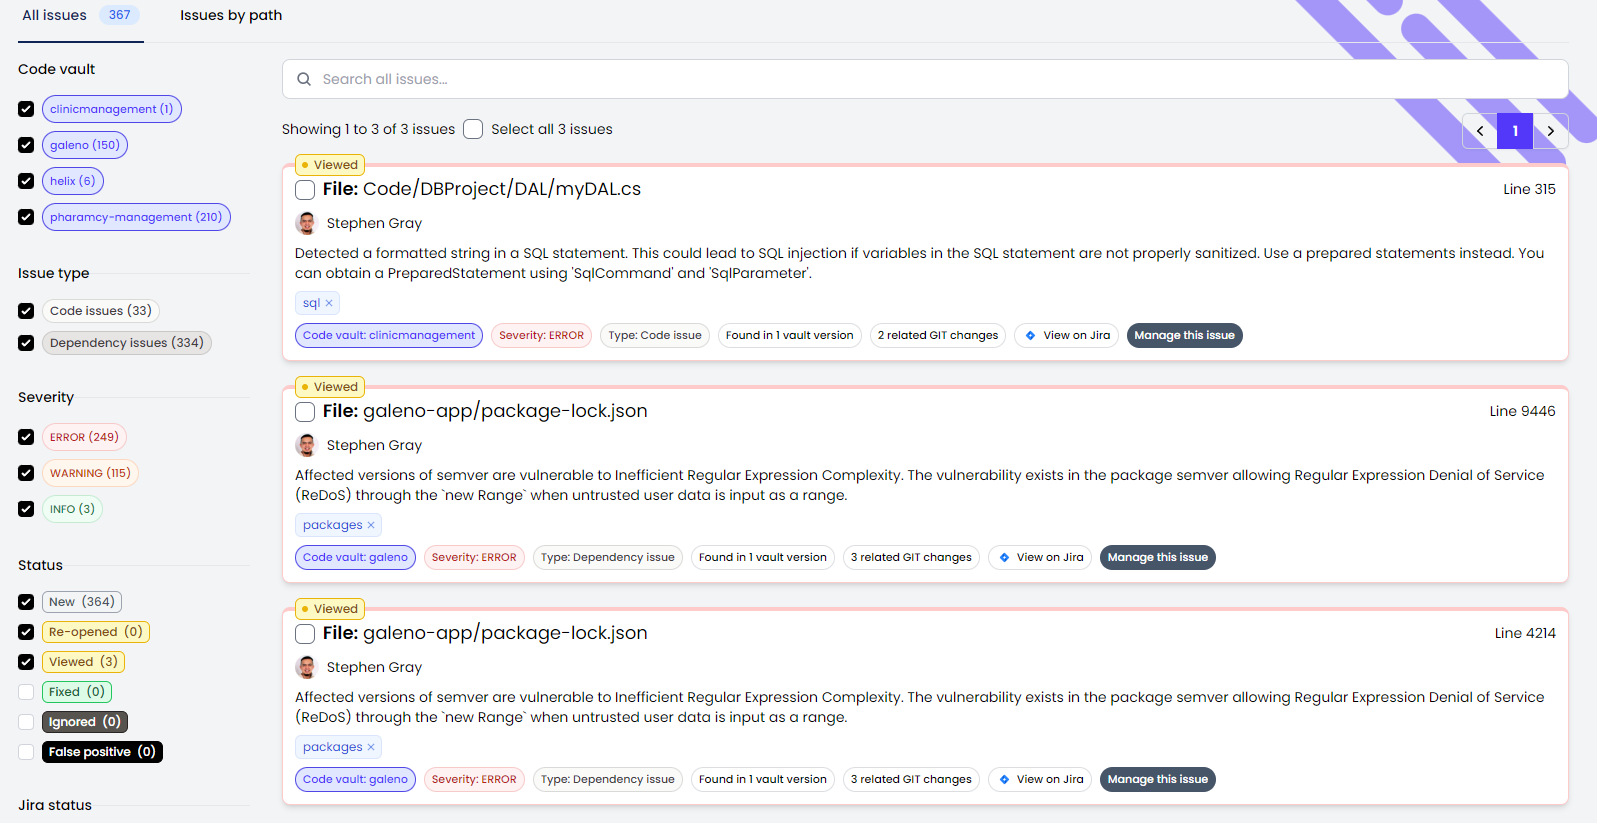
The new features include functionality that users have come to expect from other security issue management services
Custom statuses (fixed, false positive, ignore)
User comments
User assignment
Custom tagging
File content viewing with lines related to the issue highlighted
Viewing other occurrences of the same or similar issues in other files
Filters for all of the above
But we’ve also been able to add some exciting new features not found elsewhere, which we’re uniquely positioned to do due to the data and analysis we’re already doing for users’ codebases
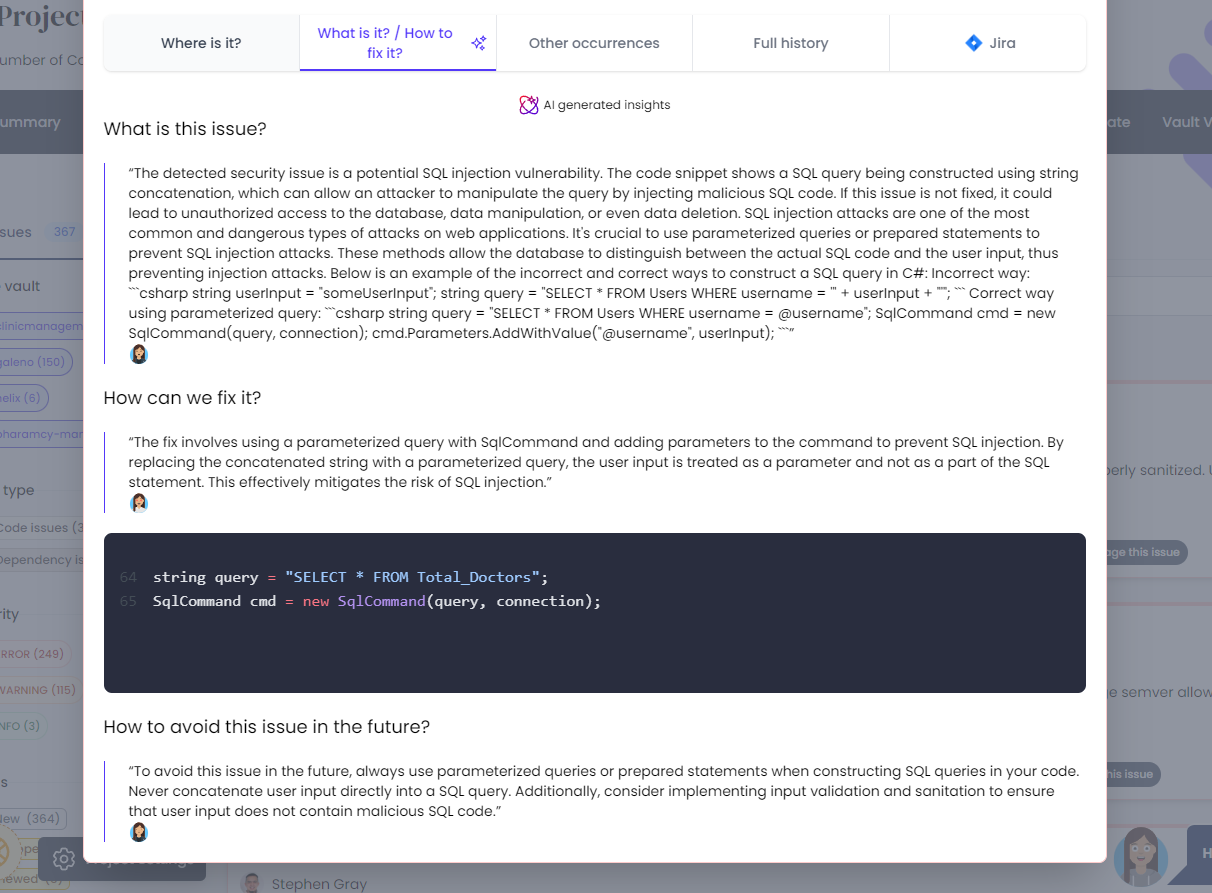
AI explanations and suggested fixes
When viewing a single issue, Ada will explain what the issue is, suggest a potential fix (both explaining the fix and with a code suggestion), and suggest how to avoid issues like this in the future.
Combined history analysis for every issue
We show a combined timeline of an issue’s history, combining all of the data we’re already analysing on the related code.
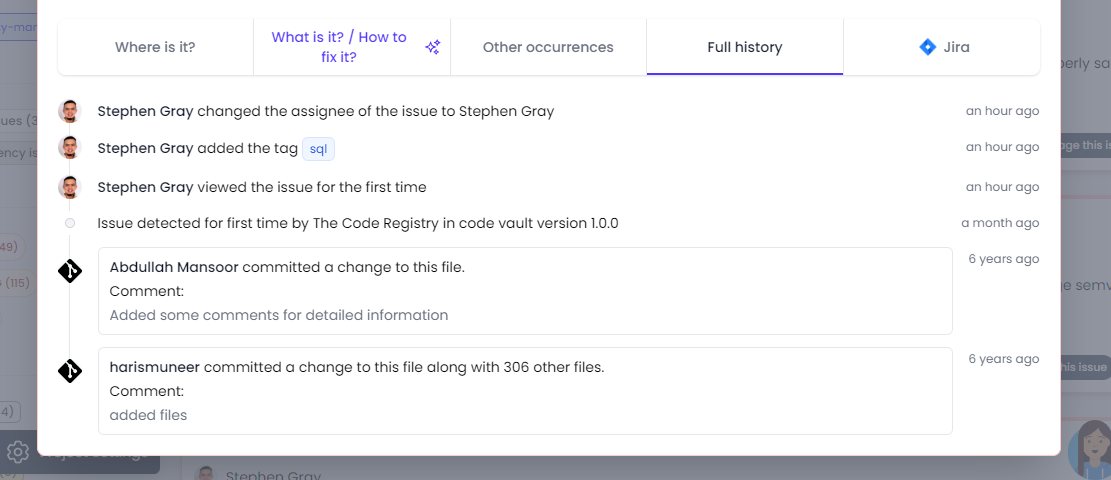
The timeline includes any related GIT changes and by which developers (so you can get an idea of who’s been working on that particular area of code), which code vault replication it was first detected in our platform, and whether the issue was fixed or still found at each code replication. It also includes any custom tags, comments, and so on from any user.
Automated updating of security issues after code replications
This is a very useful and powerful feature — when your scheduled (or manual) code replications are completed, we check for the following
If any security issues are no longer found, we automatically mark them as fixed and add a comment.
If any security issues have been marked as fixed by a user but are still there in the new code replication, we automatically re-open them and add a comment.
Integration with 40+ ticketing systems, through our partnership with Merge.dev
We’ve partnered with Merge.dev and implemented their unified API service so our users can integrate their ticketing system of choice into our platform.
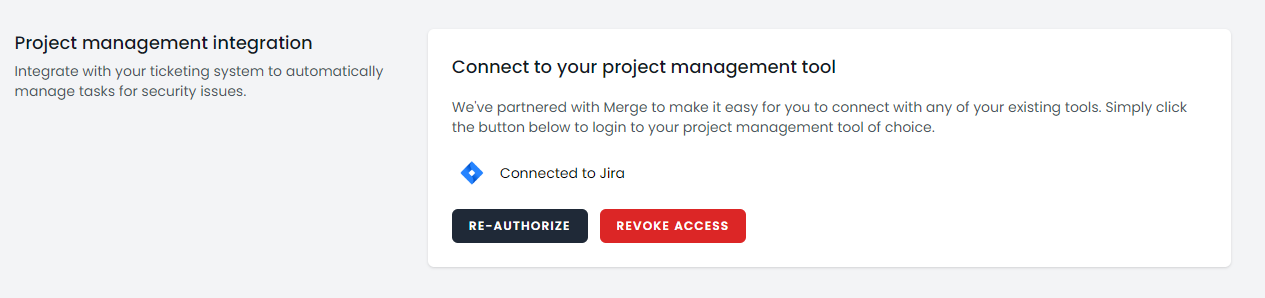
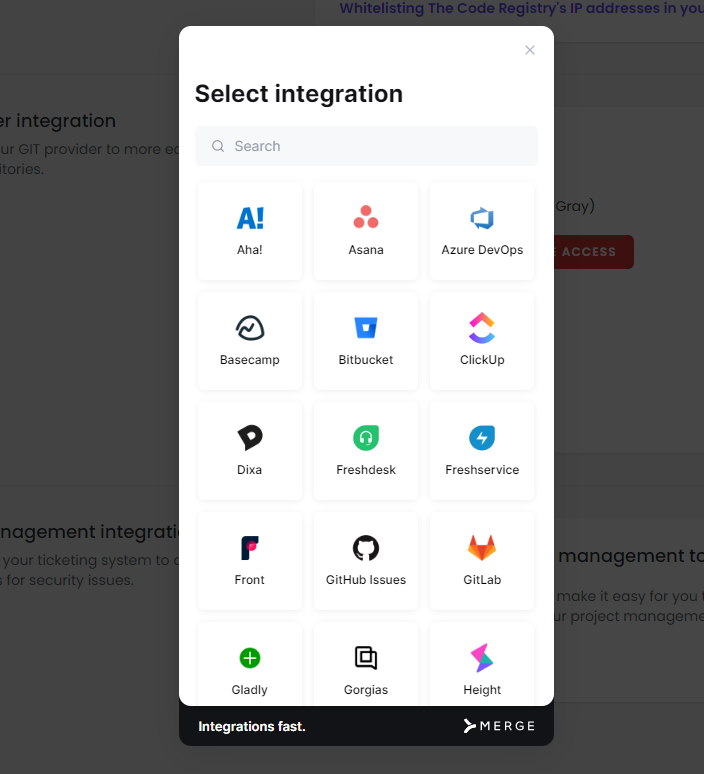
So whether you use Jira, ClickUp, Asana, or many more, you can push security issues into those systems as tickets to be worked on. Once an issue is synced with a ticketing system, any actions on our platform are mirrored into that system too — for example, comments, or marking a ticket as fixed.
And it’s a two-way integration, which means once per day any updates from your ticketing system are also mirrored in The Code Registry. Your developers can complete the issues in their normal workflow, and you’ll see the updates in The Code Registry automatically.
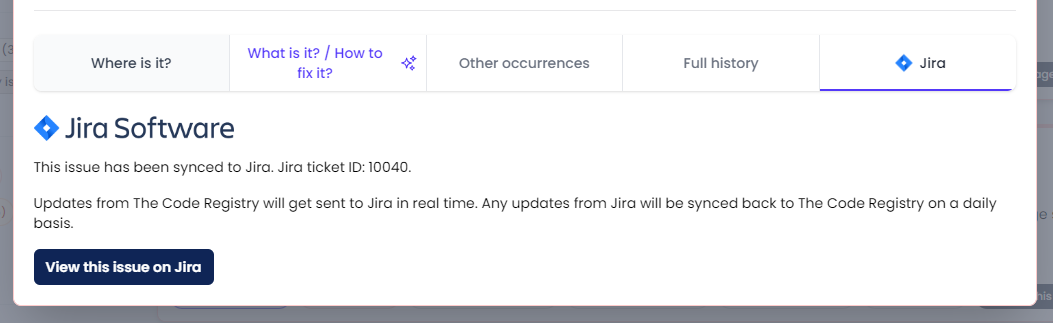
You can find this integration in the revamped “Integrations” tab on the “Team Settings” page. And because of our combined project-level view of all codebases in a project, all of the above data, filters, and issue management can be done across an entire project — whether that’s a single code vault or 20.
BUG FIXES
- Fixed a bug where very long component or component vendor names caused layout issues in PDF reports.
- Fixed a bug where searching for partial GIT repo branch names returned valid results (i.e. searching for feature-name matched feature/feature-name).
FROM COMPLEXITY TO CLARITY
Move from uncertainty to complete code confidence.
Get the independent intelligence you need to understand, verify and protect your software.
Book a demo